The only reason why I hesitate to recommend Ubiquiti cameras is even their cheapest offerings are kind of expensive.
And although you can run isolated from the Internet, managing updates is a bit painful. (Ask me how I know)
The only reason why I hesitate to recommend Ubiquiti cameras is even their cheapest offerings are kind of expensive.
And although you can run isolated from the Internet, managing updates is a bit painful. (Ask me how I know)
They gave POE cameras that will just work with an Ethernet cable (although they gave weird POE requirements). Their USB powered ones are wifi connected.
Source: I’ve had them for years and am happy with the setup.

Money doesn’t corrupt, it just exposes.
You could either set up DNS overrides on your inwards facing DNS server, leaving external resolution to something like cloudflare (with DDNS), or you have a second internal domain for internal resolution.
I chose the latter for my homelab - it’s service.lan.fqdn inside and service.fqdn on the outside. Since I use a wildcard cert, it’s still protected with TLS if I access it internally or externally.
Edit: this also solves hair pinning as your internal resolution will go to your LAN network, not your public IP
Plug your ears and drink water.
Or drink water upside down.
These are the treatments that seem to work the best
For me, I have multiple OIDC compatible systems (Proxmox, Netbox, Synology, Zabbix, Vault, etc).
So keycloak offers a SSO option to make my life easier with a single account to worry about instead of individual ones.
Plus MFA because it’s cool?
This one is bad - unauthenticated user account take over.
If you’re like me and only using it internally on a homelab, the risks are lessened, but if you expose keycloak to by the Internet - boy howdy

It’s the armpit of America!
As others have said, cap charging at ~80%. Unless you have a spare $150 for a nice UPS, I would use the built-in battery.
If you can swing compatible hardware, Security Onion is pretty great. It’s not necessary to buy their solution, it’s FOSS and there are instructions on getting it to work on proxmox.
(But you need to install agents on all your VMs and servers, and ideally do port mirroring so all traffic can make it to the Security Onion box.
I had this exact fucking problem. Check if you’re using cloud-init and if there’s a holdover entry that may be overlooked.
For me, it was under the /var/run/ folder’s netplan, not the usual /etc/netplan.
I’m a huge fan of the Hitman series, and I’m hopeful for 007… But part of what makes human Hitman so fun is dressing up like a clown, bringing a fish to Paris, and knocking everyone at a hoity toity fashion show the fuck out.
I’m not sure that play style is very “Bond-ish”, but if they allow it, I’m game.
Are you an AI bot? Rambling sentences and em dashes…
Got a few commands to try from a terminal:
curl https://google.com/
curl https://<your searxng fqdn>
Try from the SearXNG terminal too.
Lastly, in the container with Apache, there should be some log directory, maybe /var/log/apache2/? Try doing a tail -f /path/to/error.log. You could also do something like docker compose logs -f and (while tailing/looking at logs), try your search again.
If all else fails, sudo journalctl -xef and/or sudo dmesg -wT may offer something interesting.
With torrents, it is generally considered to be a faux pas to not upload as well as download. Most private trackers will require that you maintain some sort of positive ratio in order to be in good standing.
In order to upload, you need to expose ports from your download client out to the internet so that others can reach you.
For news groups, you only download, so although your system is still able to reach the internet, your download client does not expose any ports to the internet.
Edit: I suppose what I was trying to communicate is that with news groups, you are at less risk for being nabbed for piracy than torrents. The nature of the torrent protocol means that you are uploading (or at least making available to upload) any data that you have already downloaded. For news groups, there is no upload.
As a bonus, if you go with newsgroups, you don’t have to expose anything to the internet!
Maybe I ditch my plans and just establish a VLAN for IoT and guests.
That’s a good starting point. Keep IoT away from your primary vlan (for all things holy don’t use VLAN ID 1). You can limit your outbound traffic for that vlan more easily if you want to cut your smart things off from the Internet.
Guest WiFi/vlan can be just a straight shot to the internet, probably no need for visitors to get to your internal services.
Eventually, you could add a DMZ where any Internet available systems like your VPN - with specific firewall rules only permitting VPN to specific locations inside your primary vlan.
It’s only the mini Pepsi cans iirc, so they aren’t as load bearing as I’d like. God willing, I’ll upgrade to fanta boxes one day.
A little late to the party, but here’s mine.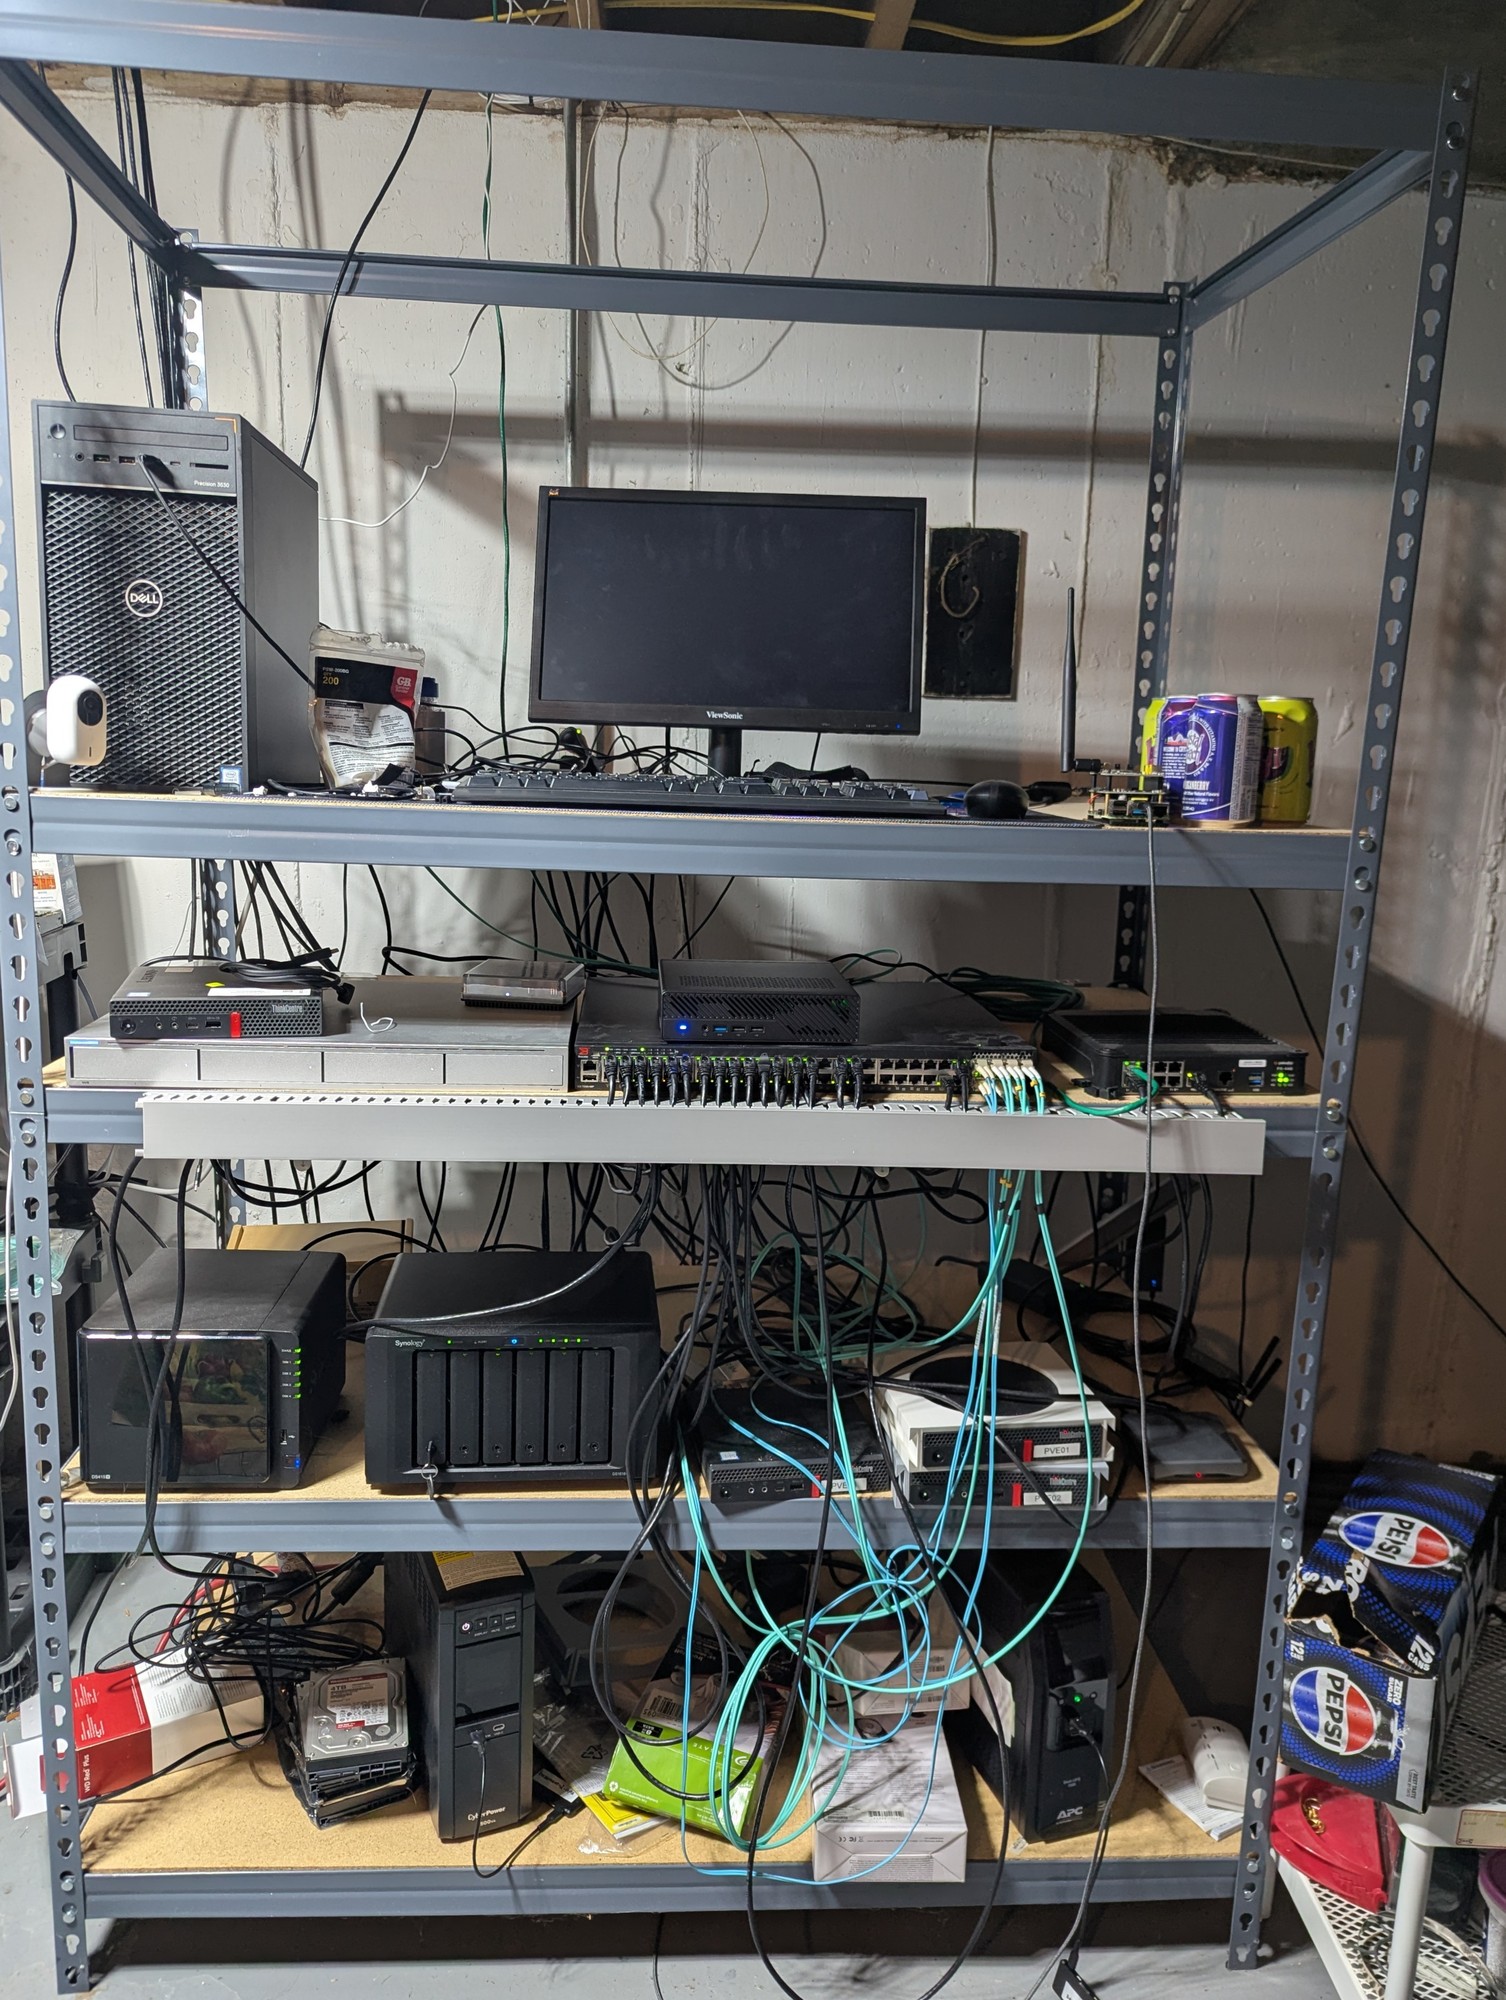
At work, I used ssh-signed certificates for Linux server access - those certs are only valid for about 15 minutes.
The whole idea of shorter lifetime certificates is to address if a certificate is compromised. (Especially for client certificates which, iirc, Let’s Encrypt no longer offers).
For a home lab? With no externally accessible services? Short-lived certs aren’t really a big deal. Nobody is going to be hacking your homelab, stealing your private keys, poisoning your internal DNS, and pointing you to a different, malicious service.